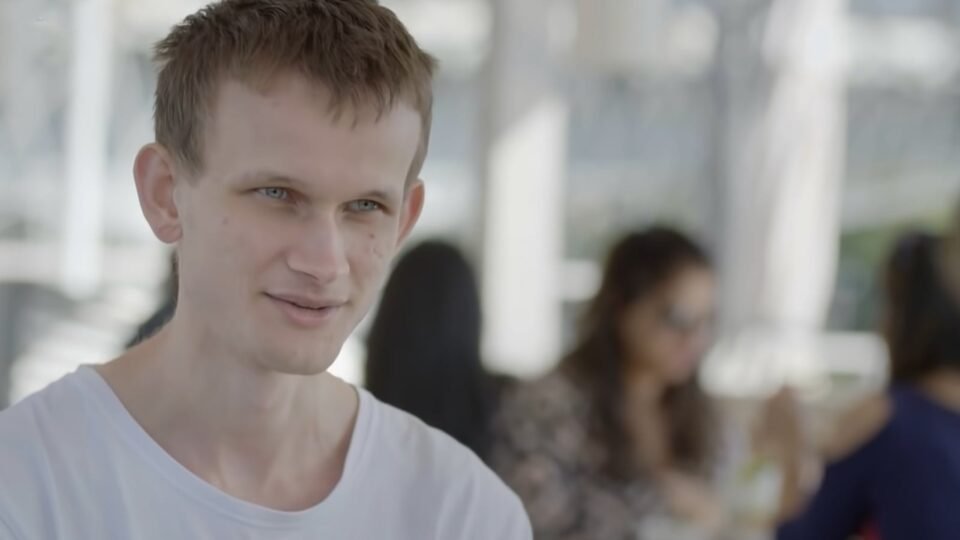
Ethereum co-founder Vitalik Buterin is pushing back against fears that increasingly capable AI will make cybersecurity unwinnable.
Ethereum co-founder Vitalik Buterin does not believe that improving artificial intelligence will eventually make cybersecurity essentially unwinnable.
Buterin is confident that the opposite could ultimately happen: AI may give defenders the tools needed to build software that is significantly harder to exploit in the first place.
“It’s an increasingly common take that AI hacking means cybersecurity is doomed. I disagree,” Buterin wrote in a lengthy and characteristically substantive social media post on Wednesday on the X social media network.
According to the Ethereum co-founder, cybersecurity should naturally favor defenders once developers begin taking full advantage of formal verification.
Buterin also tied this belief directly to his own exposure to cryptocurrency, revealing that roughly 90% of his net worth remains in crypto.
Anyone who continues to hold substantial amounts of cryptocurrency, he argued, is implicitly betting that sufficiently secure digital systems can be built despite increasingly sophisticated attackers.
“If AI can prove Navier-Stokes and FLT, then AI can prove the statement ‘this program is secure’ as a mathematical theorem,” Buterin wrote, referring to the Navier-Stokes problem and Fermat’s Last Theorem.
His argument is based on formal verification, a method of mathematically demonstrating that software satisfies specific properties.
Buterin explored the same idea extensively in his May essay, in which he described AI-assisted formal verification as a hugely transformative tool for security-critical software. However, proving that such software is secure might prove to be challenging.
Buterin used the encrypted messaging app Signal as an example to show why this could be difficult.
An attacker might attempt to forge messages, stop them from arriving, replay old messages, compromise a server, manipulate the process used to discover another user’s public key, or exploit a vulnerability in the operating system.
Other problems might arise from corrupted databases, malicious libraries, compilers, or even hardware-level information leaks.
Even if the content of a conversation remains encrypted, an attacker might still learn who is communicating. As a result, the mathematical definition of what “secure” actually means could itself become extremely complicated.
“So … even definitions can be over a thousand lines of code, and need deep careful thought to figure them out,” Buterin wrote.
Without a doubt, more capable AI systems could make finding vulnerabilities easier.
However, the same improvement in machine reasoning could also dramatically lower the cost of formally proving that software behaves according to carefully constructed security specifications.
Both sides will have AI.
More Posts About This Newsroom
u.today
-
 ‘Tokenization Is Coming to America’: Robinhood CEO Hails SEC’s Historic Ruling
-
 ‘Major Breakthrough’: Saylor Reacts to SEC’s Big Crypto Move
-
 Shiba Inu Bulls Return Amid 202-Billion SHIB Netflow
-
 Binance Alert: System Upgrade to Suspend Deposits and Withdrawals on This Date
-
 7 Out of 7 Shiba Inu (SHIB) Spot Flow Timeframes Turn Negative